🔒 When “cheap” gets expensive
Hello everyone, and welcome to a new edition of Spark Learning.
When evaluating a tool or platform for online education projects, the decision-making process is often complex. This is especially true for decision-makers who are outside the technical area and are approaching platform selection for the first time.
There are dozens of factors in play, and given the overwhelming number of options, the cost factor often tips the scales. There is a huge price disparity in the market, and it is not easy to weigh the pros and cons of each alternative without being a technology expert.
However, key factors that explain these price differences are often overlooked in this process. Today, I want to focus on a critical one: Security.
The trap of “easy and cheap”
There are many LMS options (proprietary, open source, custom-made). One alternative that initially seems cheap and quick to implement is WordPress LMS plugins.
I recently read a technical report regarding one of these free plugins that revealed something alarming. A user with advanced technical expertise detected anomalies and discovered that, upon downloading the tool, it created a hidden administrator user and a remote access “backdoor.”
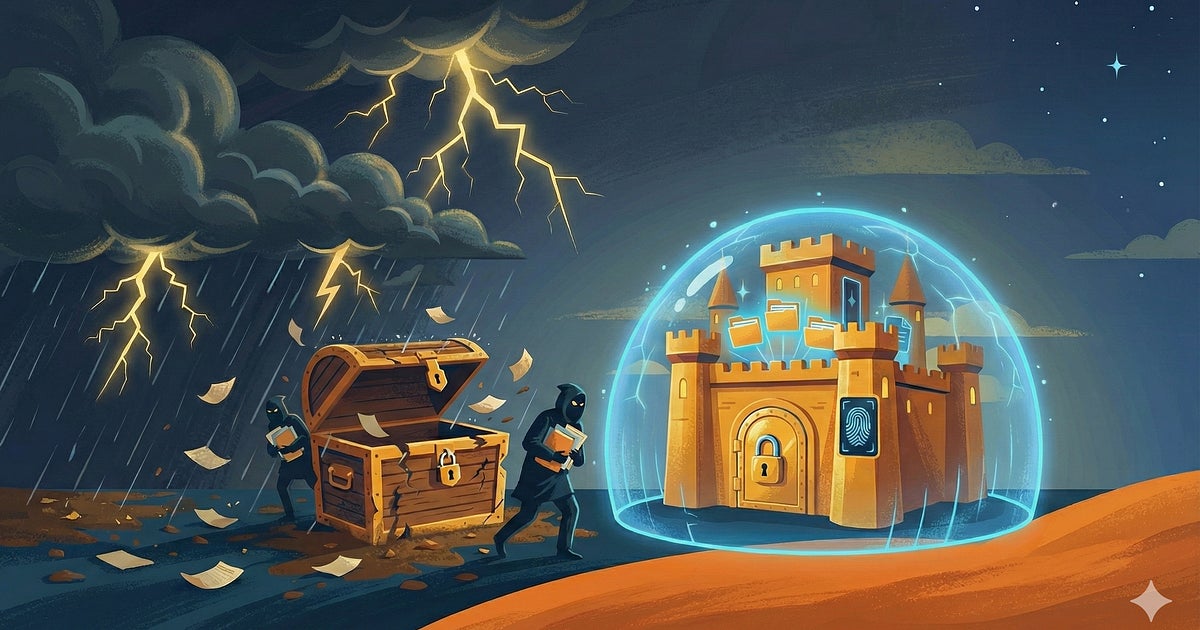
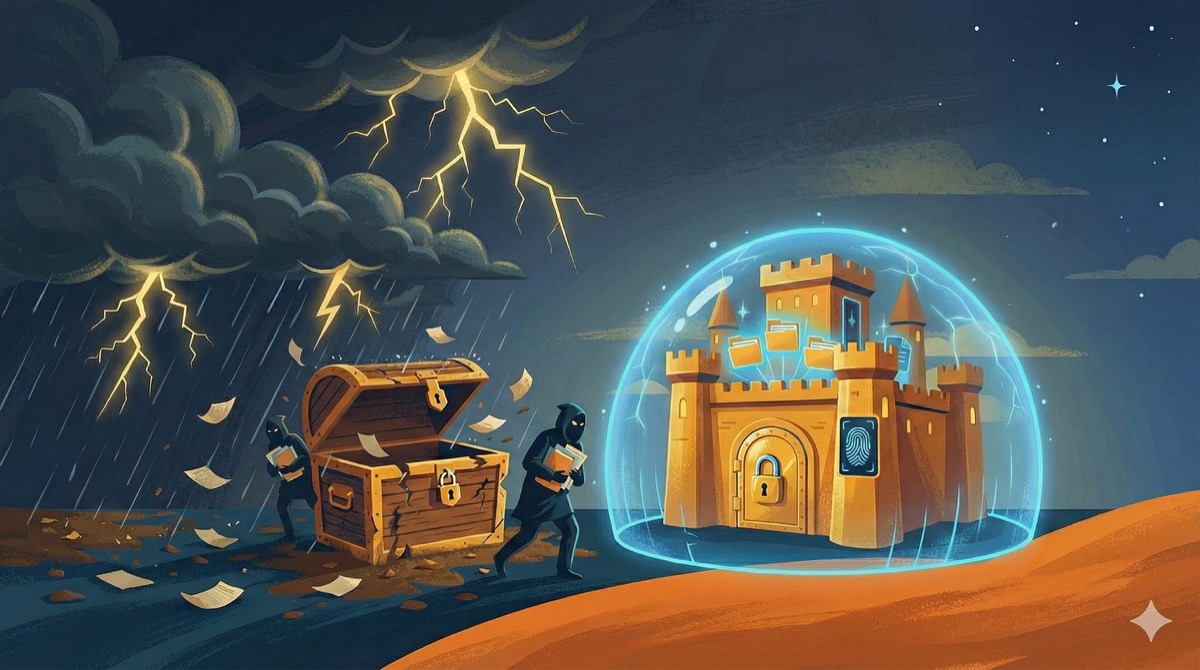
What did this mean? Basically, it handed the keys to the castle over to attackers. The impact included:
Full remote control: Managing the site from an external C2 server.
Malicious content injection: Creating posts, links, and scripts without permission.
Massive SEO Spam: Using the site to generate pages that boost attacker-owned domains.
Traffic redirection: Sending your users to scam sites.
Data theft: Collecting and sending site and environment data externally.
As the saying goes... “You get what you pay for.” The initial savings turned into a reputation and security nightmare.
A different story: Security in the first person
I want to contrast this with something we experienced this week at Aulasneo with one of our Open edX managed solution project.
In a feedback meeting with one of our partners, following the completion of a nationwide program, our point of contact shared news that filled us with pride. The project sponsor (a leading Asian technology company, known for being extremely demanding) highlighted a specific fact:
Our platform was the only one in the program that had not suffered any data leaks.
This wasn’t luck. It is the result of understanding that real security rests on three pillars that cannot be missing in a serious project:
A robust system: Pretty software isn’t enough; the underlying architecture must be solid. We use Open edX hosted on AWS cloud infrastructure, ensuring world-class standards.
A reliable provider taking basic (and advanced) measures: Security is an ongoing process. You need a tech partner who proactively applies patches, updates systems, and encrypts data—not just reactively.
A mitigation plan for emergencies: Incidents can happen. The difference between a scare and a catastrophe is having a clear, tested protocol to act immediately and neutralize threats before they escalate.
Apples to Apples
As my primary school teacher used to say: you need to compare “apples to apples.”
Not all platforms are created equal. At Aulasneo, we ensure our partners can develop their online training initiatives professionally, knowing that their users’ data—and their own reputation—are safe.
Do you feel your current security situation is fragile or unclear? Let’s talk.
Let’s see if we can collaborate to provide the leap in quality and professionalism your projects deserve.